How Salesforce Applications Evolve with AI
Salesforce is evolving from explicit CRM automation to AI-assisted work, changing how teams design context, authority, transactions, integrations, and proof of outcome.
How Salesforce Applications Evolve with AI
From CRM Automation to AI-Assisted Work
Salesforce has been the CRM application platform for many companies for decades. Teams have built business behavior there with objects, fields, metadata, Flow, Apex, approvals, reports, APIs, and events. That history matters because AI is not arriving on an empty platform.
AI changes how work enters that application. A person used to choose a screen, button, report, workflow, or explicit automation path. An agent can now interpret a request, gather context, select a capability, and coordinate several steps before the Salesforce runtime executes them.
That does not replace the Salesforce application. It adds a model-mediated decision layer: the model interprets intent and proposes a bounded operation, while the Salesforce runtime still decides whether and how that operation executes. The selected action still enters the platform’s identity, metadata, validation, transaction, limit, API, event, and deployment rules.
A request such as “review this opportunity, check the current price, update the record, create a follow-up task, and notify the pricing system” sounds like one business action. In the system, it is a path from intent to context, capability selection, authorization, deterministic execution, external ownership, and verified outcome.
The useful question is how a Salesforce-native application changes from explicit CRM automation to AI-assisted work, and what the design must still make clear as the platform evolves.
This is the opening post in AI-Native Architecture on Salesforce. It establishes that evolution and the responsibilities that remain durable through it.
About This Series
AI-Native Architecture on Salesforce follows how the application platform changes as AI becomes part of the Salesforce runtime. Each article starts with a capability Salesforce teams already know how to build, then examines what AI changes now and what the platform may coordinate next.
The series focuses on decisions that product names can hide: how intent enters the application, where context comes from, which capabilities remain deterministic, where authority lives, what crosses a real system boundary, and how failures and time affect the design.
Each post stands on its own and extends the picture of Salesforce as an application platform that is changing from the inside.
The series’ central question is:
What did Salesforce teams build explicitly before AI, what changes now, what may the platform coordinate next, and what responsibilities must remain clear?
Salesforce Before AI Joined the Loop
Before AI became a participant in the runtime, Salesforce teams already had a rich way to build CRM behavior.
Objects and metadata established the shape of the application. Fields, relationships, validation rules, record types, page behavior, and permissions made the CRM model executable rather than merely descriptive.
Flow, Apex, approvals, and other automation surfaces made business behavior explicit. A person or known system initiated a path, and people building the application could usually identify which rules, actions, and transactions would run.
APIs and events connected Salesforce to pricing, payment, fulfillment, analytics, and other systems. The local transaction, remote call, event publication, and downstream work had different owners and failure behavior, even when a user experienced them as one process.
Deployment separated metadata from data and made configuration, credentials, permissions, reference values, and external dependencies part of the lifecycle. Salesforce did not remove architecture. It made more of the application executable through platform behavior.
That is the starting point for understanding the AI shift. The platform already owns a large part of the application’s behavior. AI adds a new way to enter and coordinate that behavior.
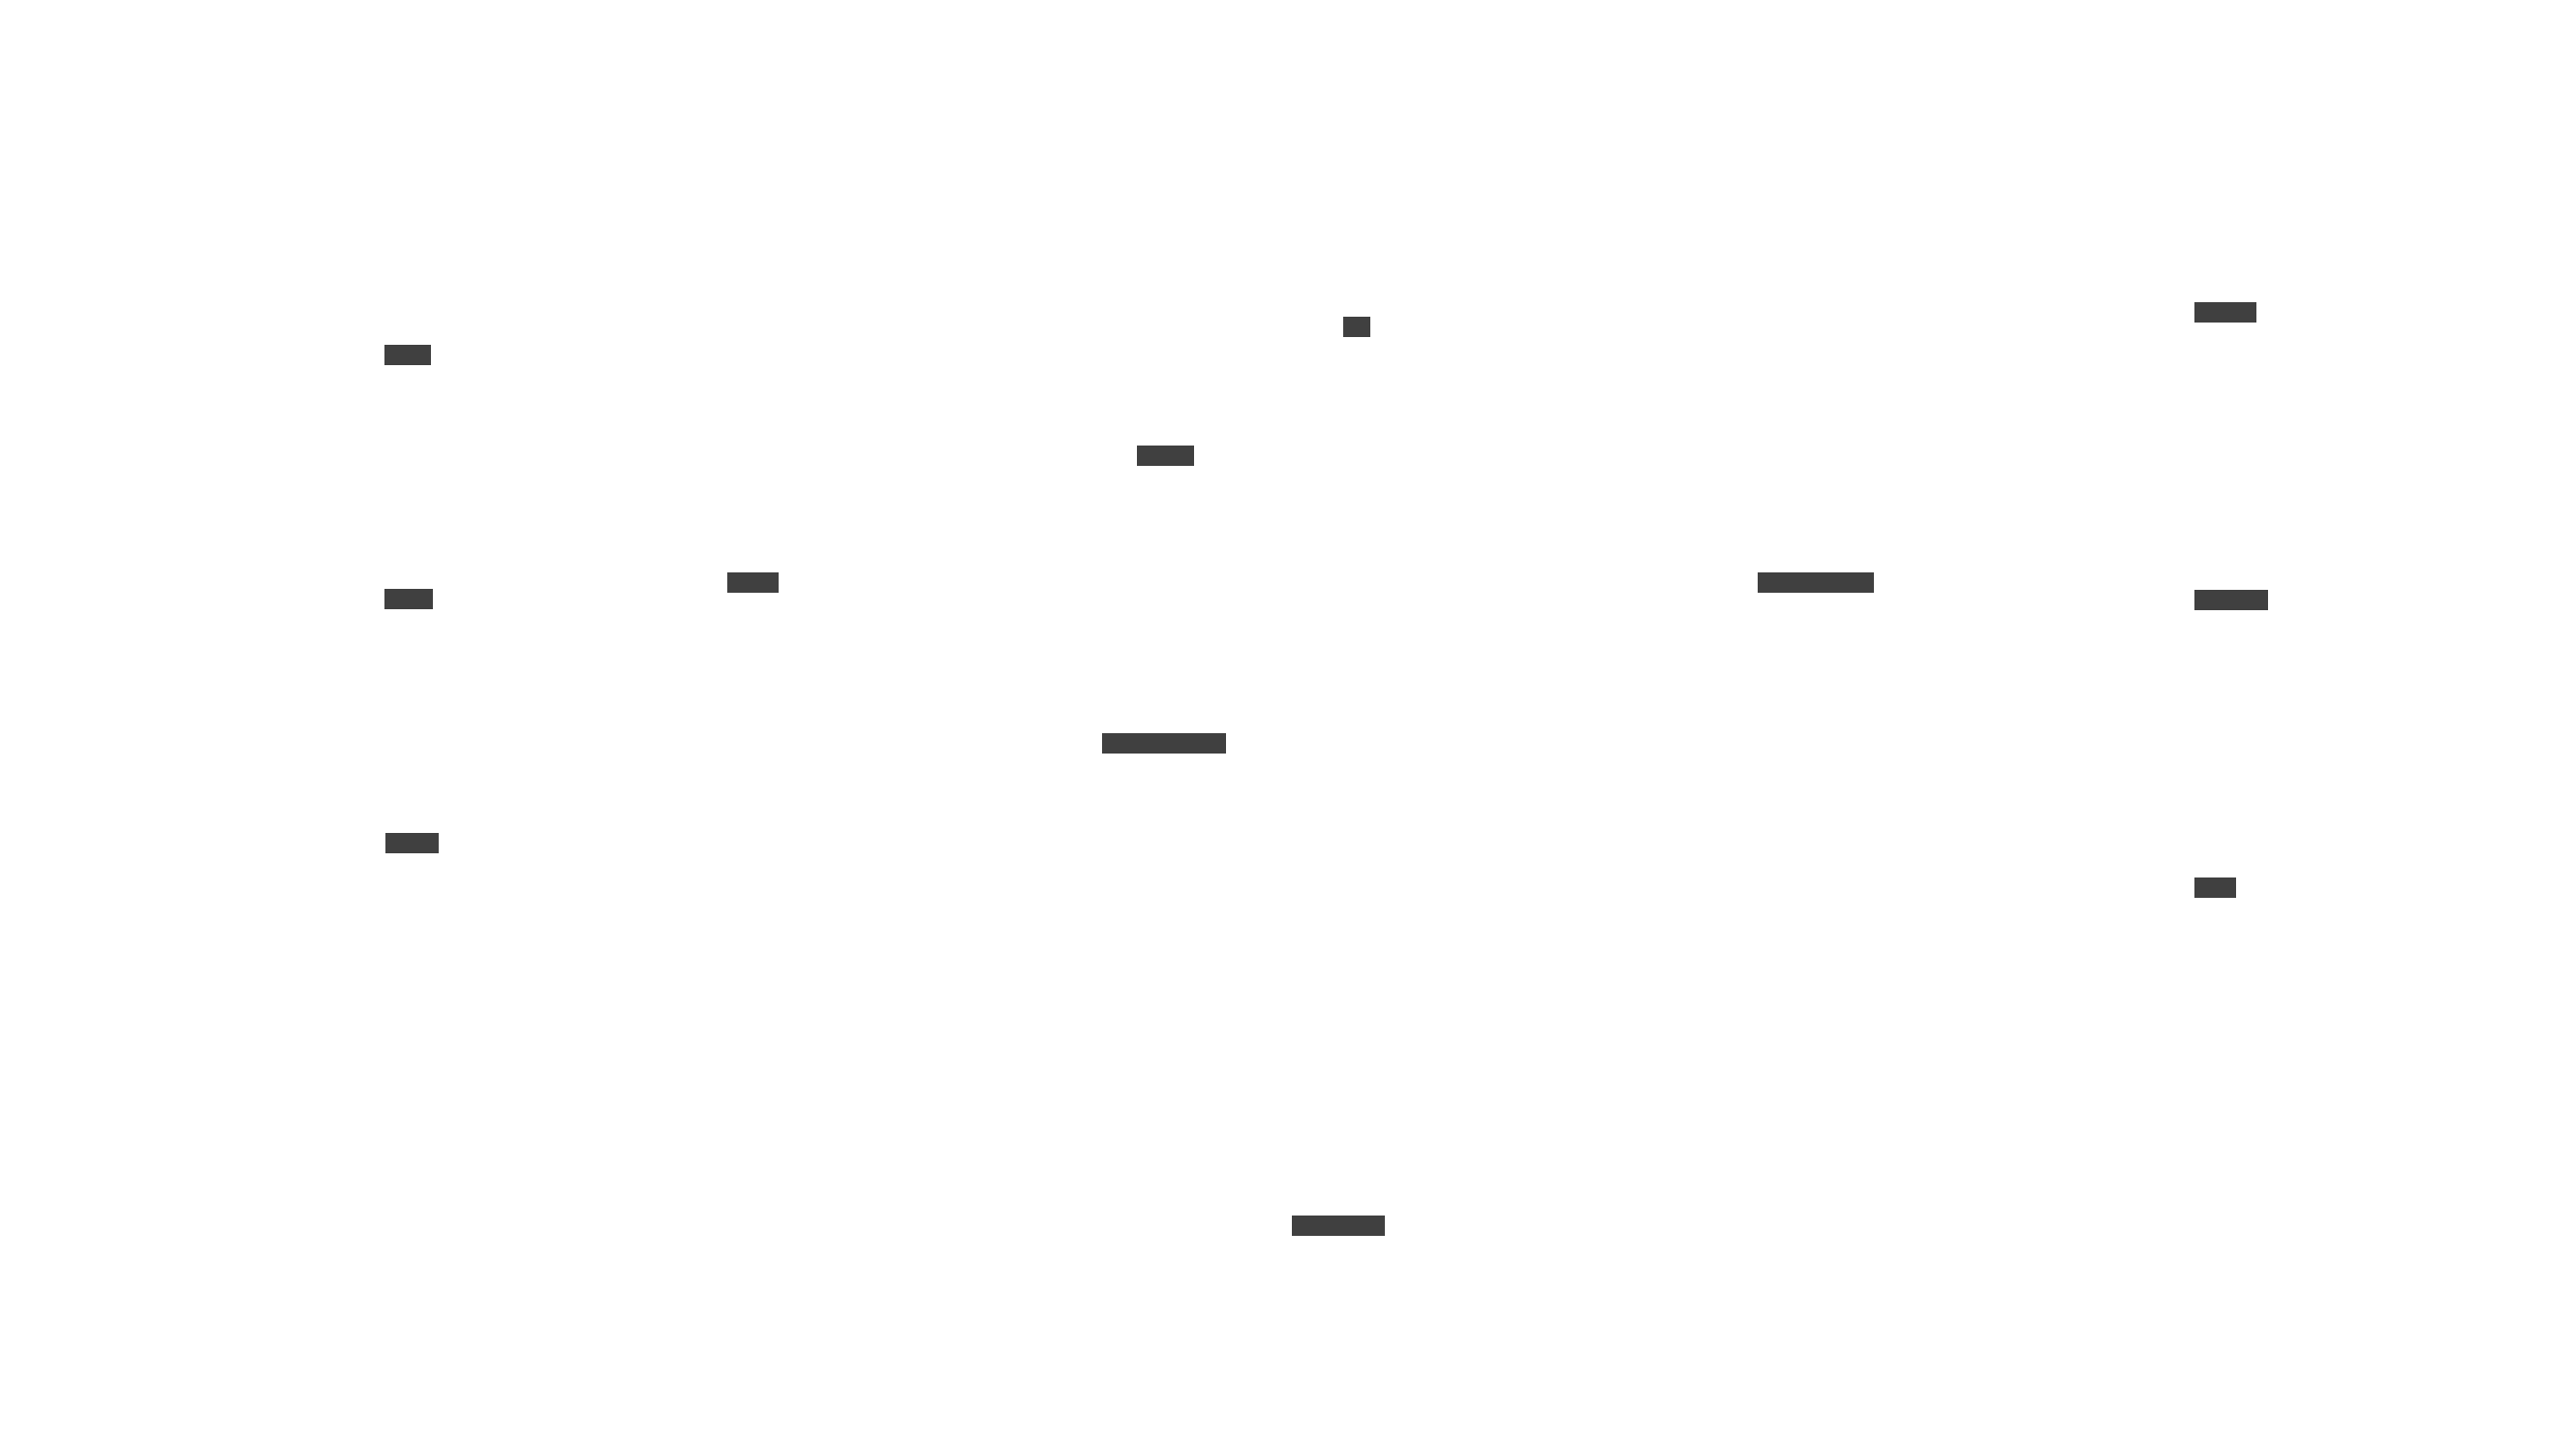
The Salesforce application evolves from explicit automation to agent-assisted work. The platform may coordinate more over time, but authority, transactions, time, and evidence still need clear owners.
Today: AI Enters the Existing Salesforce Application
An agent introduces a variable decision layer before the existing Salesforce machinery runs. The model can interpret a request and propose a path, but the platform still has to govern the action.
The path is now easier to describe as five separate stages:
user intent
  -> agent interpretation and context
  -> capability proposal
  -> authorized Salesforce execution
  -> verified business outcome
The stages are related, but they are not interchangeable.
Here, a capability means a bounded operation the Salesforce runtime can authorize, execute, and report on. It is more specific than a general instruction and more consequential than a model suggestion.
An interpretation is not a capability. A capability proposal is not permission. Permission is not execution. Execution is not proof that the requested business outcome occurred.
The current Salesforce surface may change the first two stages by helping a model understand intent and select a capability. The established platform surfaces still govern the later stages: metadata, record access, validation, Flow, Apex, transactions, limits, APIs, events, and deployment.
The existing runtime still governs the action
When AI enters the application, the effective program becomes larger, not smaller. Objects, fields, permissions, flows, Apex, action definitions, prompts, agent instructions, and integration configuration can all influence the result. A vague capability description can lead to the wrong selection; a correct selection can still be rejected by sharing, field access, validation, or approval rules.
An agent action that invokes Flow or Apex enters a Salesforce execution context with validation, order-of-execution behavior, and limits. A governor limit, the platform’s cap on work in that context, can determine whether the design is synchronous, asynchronous, batched, or safely retryable.
External services and event subscribers remain separate owners. They have their own authority, availability, data, capacity, and response contracts. API choice, event timing, retries, duplicate delivery, and after-commit behavior remain part of the business design.
Identity remains explicit. A model can propose an action, but it does not become the authority merely because it selected a tool. The runtime still determines whose permissions, sharing rules, field access, consent, and approvals apply.
The same is true of deployment. Metadata, data, credentials, permissions, agent instructions, action definitions, prompts, Flow, Apex, integrations, and tests may move through different mechanisms, but they form one effective application and must be verified together.
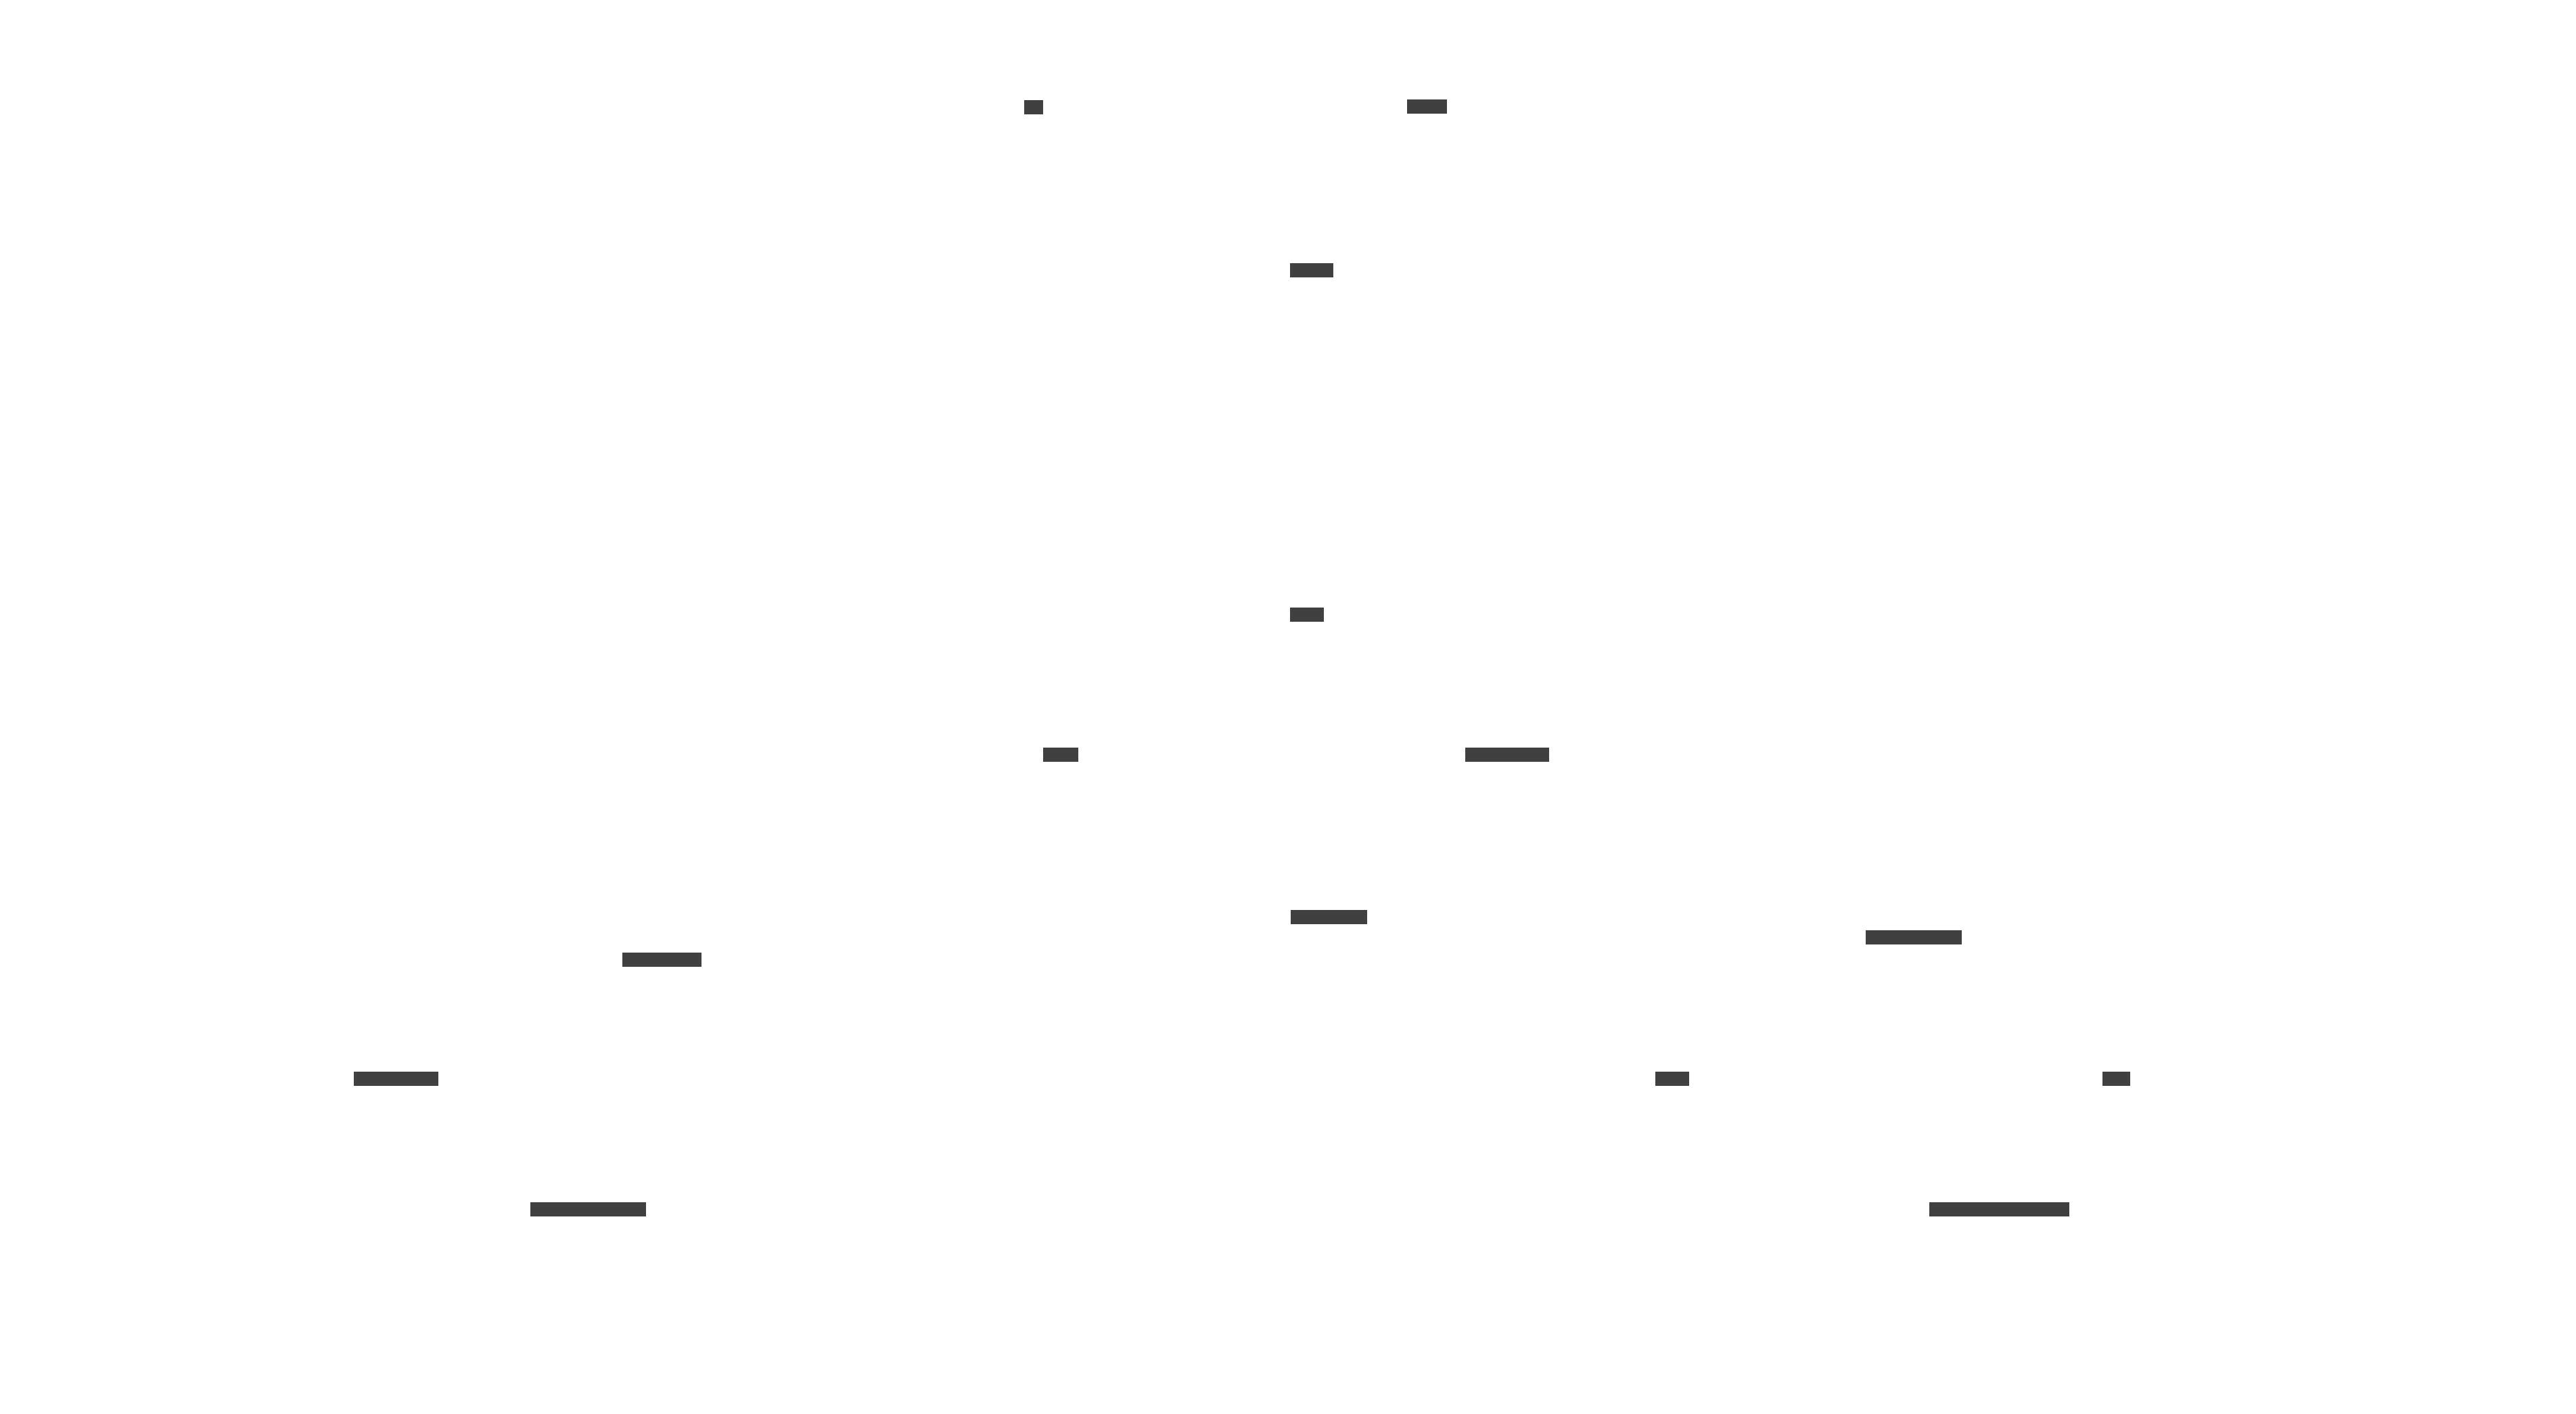
When an agent enters Salesforce, the platform governs the local action while external services, event delivery, and verified outcomes remain separate responsibilities.
A Concrete Evolution: Opportunity Review
The diagram shows the shape of the change. The opportunity process makes it concrete.
Before AI: explicit CRM automation
A sales user opens an opportunity, reviews the record, checks a price, changes a field, and creates a follow-up task. A validation rule or Flow checks the write. Apex may handle a more involved calculation. An event or API call may notify another system.
The path is not necessarily simple, but the source of intent is clear. A person or known automation starts a named operation. The sequence can be drawn from the user action through the Salesforce transaction and any downstream boundary.
Today: an agent proposes the path
The user can express the outcome instead of selecting each operation. The agent interprets the request, retrieves the relevant opportunity and pricing context, and proposes a capability or sequence of capabilities.
The proposal still needs a contract. It must identify the opportunity, constrain the inputs, state what the action may change, and return a result that the runtime and the user can understand. The existing Salesforce runtime then applies identity, sharing, validation, Flow, Apex, transaction, and limit rules.
The change is significant, but it is specific. The model helps with intent and selection. It does not own the record, the permission, the local commit, the remote pricing result, or the definition of done.
Tomorrow: more of the coordination may move into the platform
The platform may eventually provide more of the context assembly, capability composition, long-running coordination, and outcome handling around a Salesforce-native process. That is a direction for design, not a promise about a particular product release.
The durable preparation is to keep the responsibilities visible now. Define capabilities with clear inputs and outputs. Keep authorization separate from model choice. Make transaction and event boundaries explicit. Record evidence for the business outcome. Then the platform can absorb more coordination without making the system’s behavior unknowable.
The future question is therefore not whether an agent replaces Flow or Apex. It is which parts of the current Salesforce application become platform-coordinated while policy, authority, data meaning, and evidence remain explicit responsibilities.
Under the Hood: The Boundary Checklist
For each capability, write down the following before choosing a feature or exposing an action to an agent:
| Boundary | Question to answer | Design consequence |
|---|---|---|
| Identity | Which human, agent, integration, or service principal is acting? | Define permissions, sharing, field access, consent, and audit identity. |
| Context | Which records and external facts are relevant, current, and authorized? | Separate retrieval and grounding from the authority to change state. |
| Transaction | What must commit or roll back together? | Keep the local atomic unit small and explicit. |
| Limits | Which per-transaction, org-wide, API, event, or agent limits apply? | Choose batching, queues, async processing, or an external worker deliberately. |
| API | Which contract fits the volume, direction, and timing? | Select the API by workload, then plan versions, errors, and capacity. |
| External dependency | Who owns the pricing, payment, fulfillment, or policy result? | Model timeout, partial success, retry, idempotency, and reconciliation. |
| Event | When is the event published, and how long can it be replayed? | Decide whether subscribers may observe uncommitted state and how duplicates are handled. |
| Deployment | Which metadata, data, credentials, and reference values must move together? | Treat deployment as a lifecycle with prerequisites, tests, and drift control. |
| Evidence | What proves the requested business outcome happened? | Record proposal, authorization, execution, external response, commit, and verification separately. |
This checklist is meant to survive changes in product names and platform surfaces. The seams remain.
What to Design Now
Draw Salesforce as an active runtime boundary, not a feature box. Put transactions, metadata, identity, limits, APIs, events, and external systems on the diagram. Choose each capability by its semantics, scale, authority, recovery behavior, and lifecycle.
Version the metadata that defines behavior. Test with realistic permission contexts and representative data. For agentic paths, test selection separately from execution, then verify the side effect and the business outcome.
Make status visible: suggested, awaiting approval, processing, committed, failed, and verified are different states. Assign clear owners for configuration, deployment, capacity, external dependencies, identity, and reconciliation. During an incident, ask which boundary failed and what business state remains uncertain.
Failure Modes
False atomism
People describe a multi-system path as one operation because the user expressed it in one sentence. The result is missing retry, compensation, and status design.
Hidden limit coupling
Several automations each fit their local test. Together they exhaust a per-transaction or org-wide limit. The fix is usually decomposition, batching, or a new boundary, not a larger prompt.
Permission by implication
The agent can see a capability description, so people assume it can safely use the capability. The runtime still needs explicit identity, sharing, field access, policy, and approval checks.
Boundary success assumed
An event may be published before the record commits, or an external service may time out after the local transaction succeeds. Publish timing, retry, idempotency, and reconciliation are part of the business contract.
Metadata or API drift
The repository, org, and integration can disagree. A deployment may change only part of the effective behavior, or an API may no longer fit the workload. Source control, dependency awareness, capacity checks, version review, and post-deployment verification are the remedy.
Response mistaken for outcome
The agent writes a convincing summary, but no system of record or independent check confirms what happened. The response is evidence of communication, not necessarily evidence of completion.
Build It Once
The reusable artifact for this series is a one-page platform boundary worksheet.
For each capability, record:
intent:
context:
acting_principal:
authorized_capability:
local_transaction:
platform_limits:
api_or_event_boundary:
external_owner:
retry_and_idempotency:
deployment_units:
verified_outcome:
operational_owner:
The point is not the exact field names. The point is to describe the seams before selecting or exposing a capability. The worksheet can sit beside a Flow, an Apex action, an agent action, an integration contract, or an external service design.
Will This Term Survive?
Terminology durability: the phrase “AI-Native Architecture on Salesforce” names the series’ architectural scope, while its product vocabulary will change. “Salesforce application evolution” and “platform-native architecture” are more durable because they describe a relationship rather than a release.
The durable pattern is Salesforce’s continued absorption of application behavior into a governed platform. The current shift is that agents add a variable decision layer inside that application. The names will move. The need to model authority, state, time, limits, and evidence will not.
Where It Fits in the Map
This opening post establishes the platform substrate for the series:
platform substrate
  -> metadata and data
  -> transactions and limits
  -> identity and authority
  -> APIs and events
  -> deployment and evidence
Future posts will extend this boundary analysis as new articles are written.
The recurring question is:
What did teams build explicitly before AI, what does AI change in the Salesforce runtime now, what might the platform absorb next, and what does the team still have to own?
Sources
- Salesforce Architects: Architecture Basics
- Salesforce Architects: Well-Architected Framework
- Salesforce Developers: API Request Limits and Allocations
- Salesforce Developers: Enterprise Messaging Platform Events
- Salesforce Developers: Platform Event Fields
- Salesforce Developers: project deploy start
- Salesforce Developers: API End-of-Life Policy
More in This Series
This is currently the first article in AI-Native Architecture on Salesforce. New article links will be added here as the series grows.
Subscribe
Get new posts by email
Enterprise architecture, AI systems, and platform strategy.